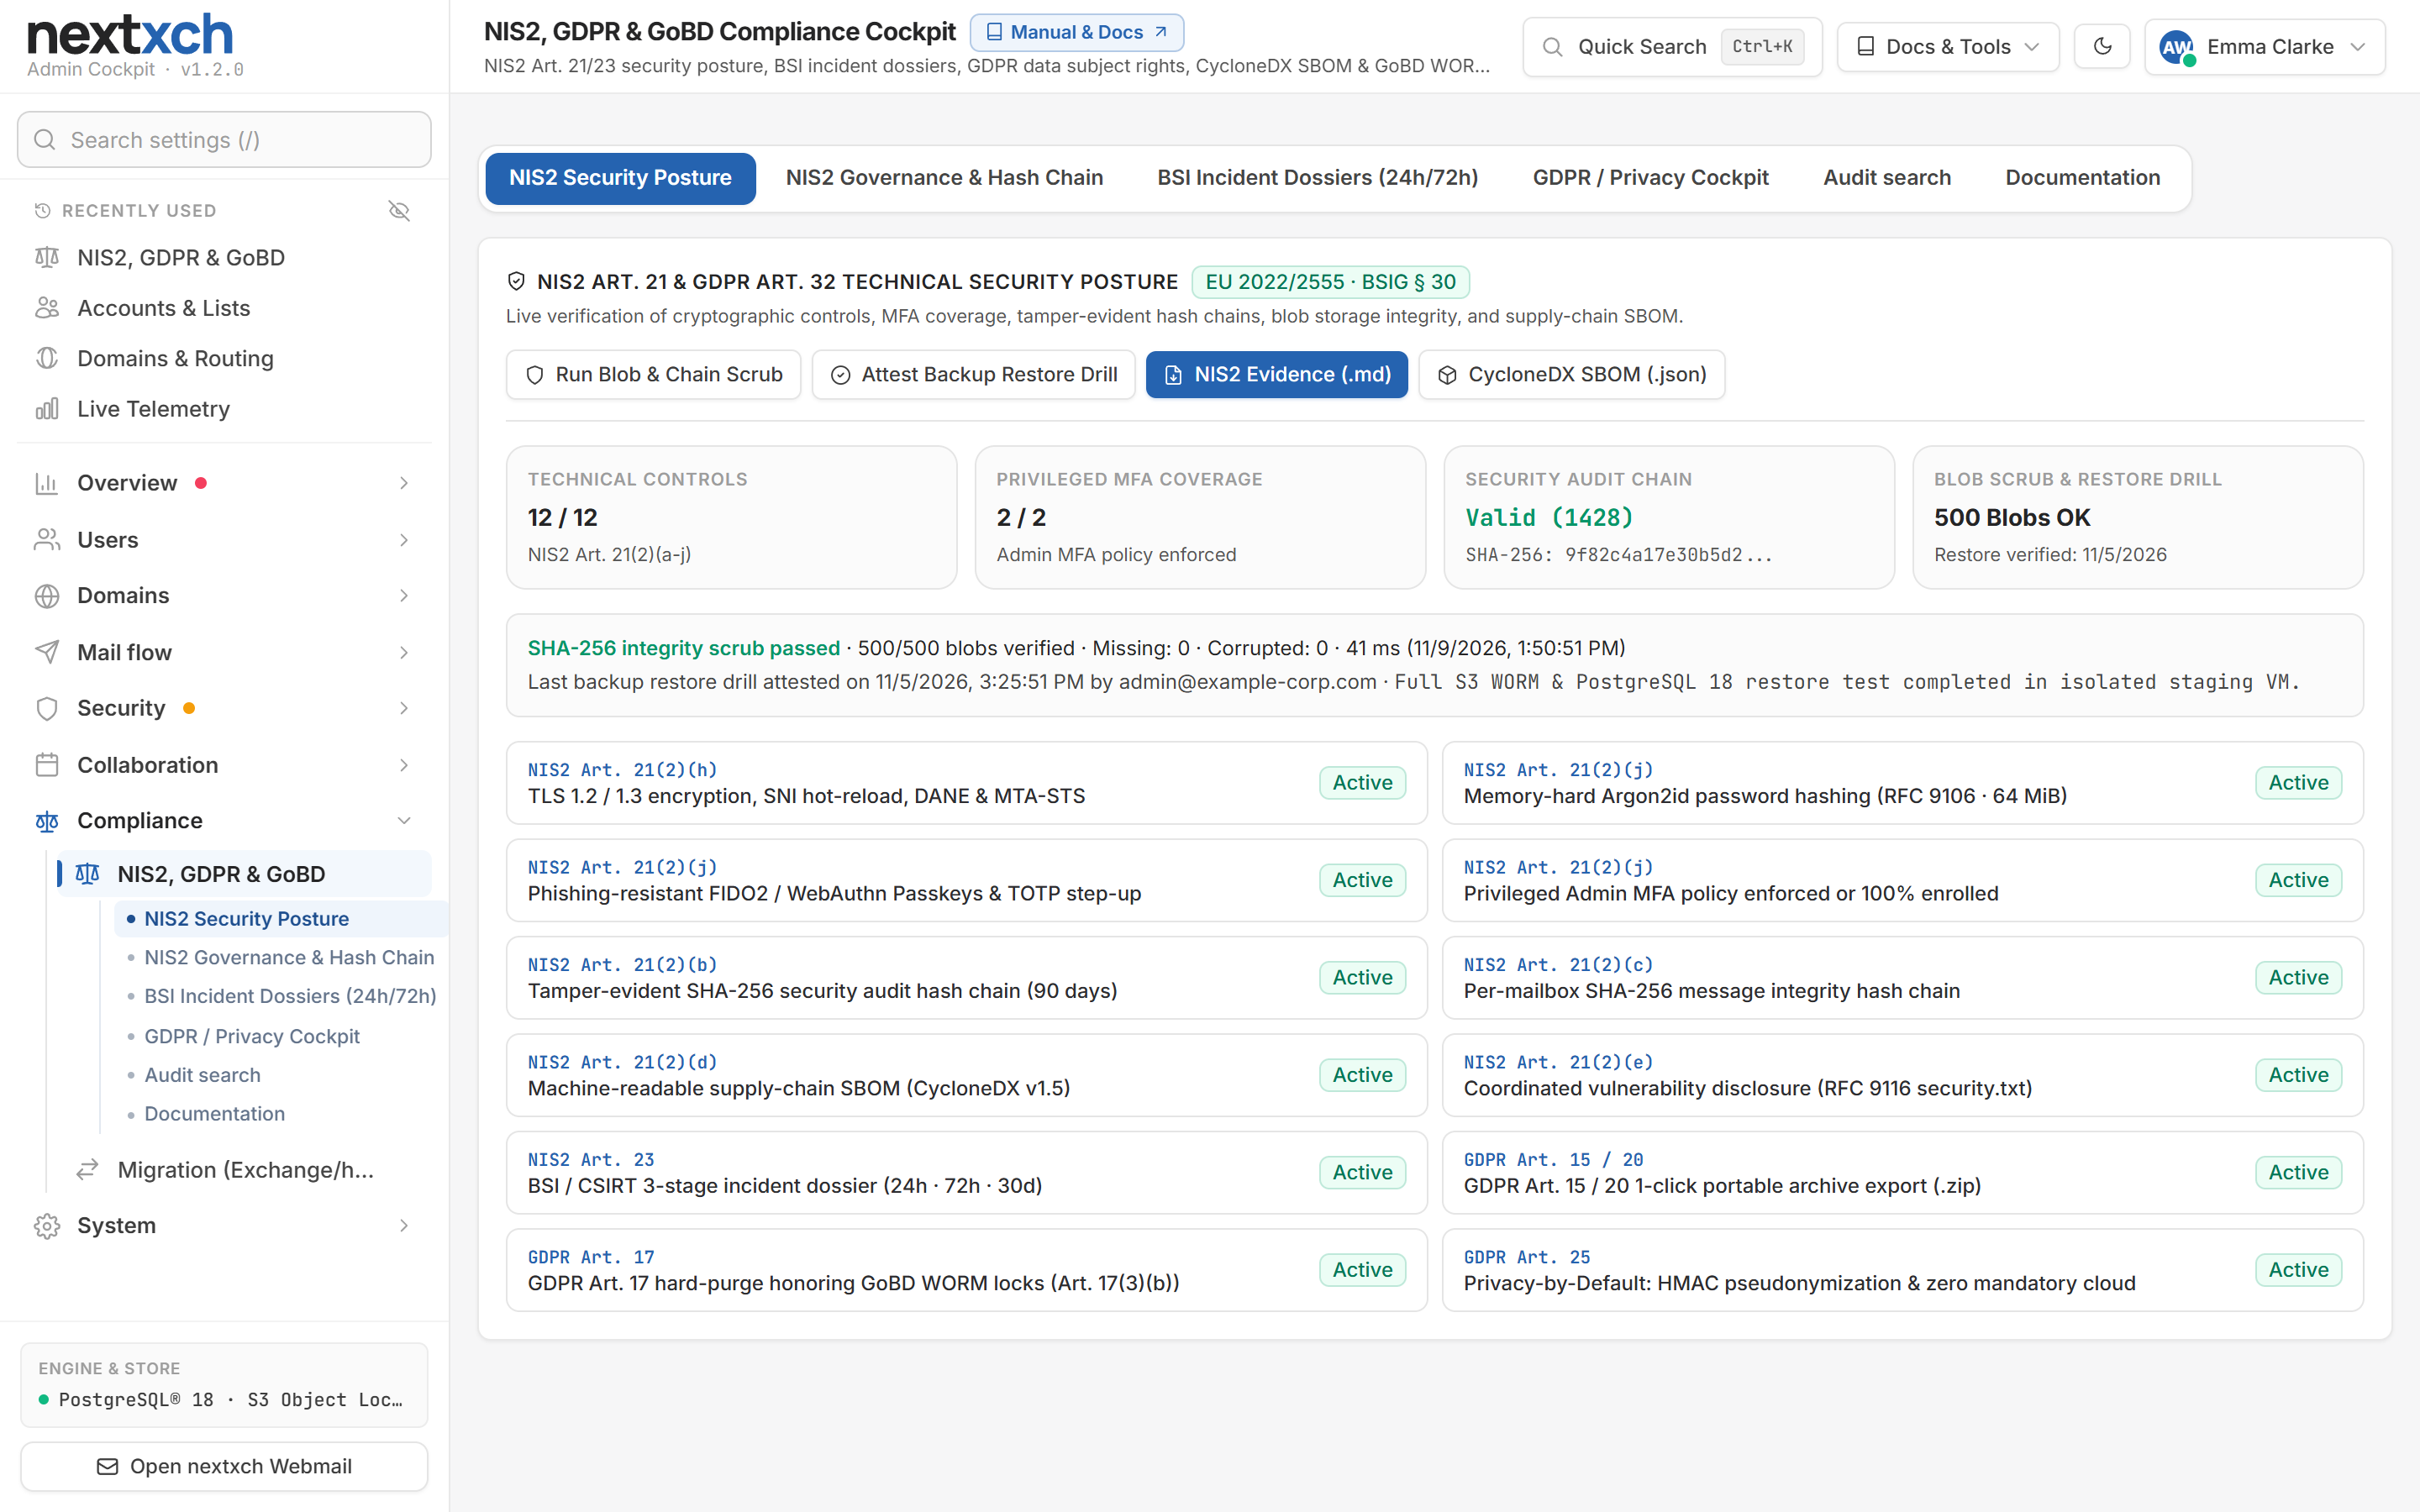

Built-In 5-Tab NIS2, GDPR & GoBD Compliance Cockpit
Live verification of all 12 technical controls under NIS2 Art. 21(2), 3-stage CSIRT incident dossier generator (24h/72h/30d), CycloneDX SBOM, GDPR Art. 15/17/20, and 10-year GoBD WORM archive.
Email, calendars, and address books sit at the center of business continuity, NIS2 audits, and GDPR inspections. nextxch combines 100% self-hosted sovereignty (zero US CLOUD Act exposure) with a built-in compliance control plane: enforceable Passkey/TOTP MFA, daily SHA-256 integrity scrubbing, 3-stage 24h/72h/30d CSIRT incident dossiers, CycloneDX SBOM export, GDPR Art. 15/17/20 automation, and GoBD WORM retention.
Live verification of all 12 technical controls under NIS2 Art. 21(2), 3-stage CSIRT incident dossier generator (24h/72h/30d), CycloneDX SBOM, GDPR Art. 15/17/20, and 10-year GoBD WORM archive.
US-operated cloud suites retain extraterritorial legal exposure (US CLOUD Act, FISA 702) and complex sub-processor chains even when hosted in EU regions. nextxch eliminates third-country exposure by design:
Runs on your own bare metal, European cloud hosts (Hetzner, netcup, IONOS, OVHcloud), or air-gapped networks. A single self-contained binary with zero external scripts, fonts, CAPTCHAs, or CDNs.
Our native nextxch mobile app connects directly over TLS to your server. Zero message content traverses Firebase (FCM) or third-party push relays, protected by biometric lock (Face ID / fingerprint) and app-switcher privacy shield.
Optionally encrypts every mailbox at rest with per-account AES-256-GCM keys, paired with built-in S/MIME, OpenPGP, Web Key Directory (WKD), DANE TLSA, and MTA-STS.
The new Outlook® for Windows and Outlook.com fetch IMAP mailboxes through Microsoft® servers, so credentials and mail end up there. nextxch detects such sign-ins on IMAP, POP3, SMTP and ActiveSync®, shows them per account and domain in the admin and, if you wish, blocks them per domain or server-wide, with a clear explanation in the mail app. In every tier.
Article 21(2) of the EU NIS2 Directive mandates ten concrete cybersecurity risk-management domains for essential and important entities. Every row below maps directly to shipped code and endpoints in nextxch:
| Statutory Mandate (NIS2 / BSIG) | Technical Enforcement in nextxch | Verifiable Endpoint / Module |
|---|---|---|
| Art. 21(2)(a) · BSIG Sec. 30(1) Policies on risk analysis and information system security |
Real-time NIS2 posture score in the Admin Cockpit (pCompliance), configurable idle and persistent session policies for Webmail and Admin (incl. optional 90-day stay-signed-in), IP security rules, persistent login history with offline GeoIP, and verifiable governance state. | GET /api/admin/compliance/overview · SessionActivityService |
| Art. 21(2)(b) · BSIG Sec. 30(2) Incident handling, detection and containment |
3-stage BSI/CSIRT incident dossier generator (24h, 72h, 30d) correlating failed logins, banned IPs, user phishing reports, and audit logs, paired with Campaign Vacuum Sweep to retroactively purge detected phishing waves across all mailboxes. | POST /api/admin/compliance/incidents · ActiveSpamDefense |
| Art. 21(2)(c) · BSIG Sec. 30(3) Business continuity, backup management and disaster recovery |
Active-active clustering on PostgreSQL® 18 or Microsoft® SQL Server® with zero Redis dependency, built-in DNS failover (Hetzner, Cloudflare), temporary SMTP 4xx responses during storage outages instead of mail loss, encrypted incremental data backup (AES-256-GCM) to local, SMB or S3 targets with Object Lock and automatic verification, configuration backup with a version before every update, bare-metal recovery on first start, declarative GitOps YAML (nextxch-cli config export/apply), and backup restore drill attestation. | POST /api/admin/compliance/backup-verify · nextxch Protect · ConfigAsCode |
| Art. 21(2)(d) · BSIG Sec. 30(4) Supply chain security and software bill of materials (SBOM) |
Runtime generation of a machine-readable CycloneDX v1.5 JSON Software Bill of Materials across all loaded assemblies, public SHA-256 checksums for every release artifact, self-contained .NET clean-room binary without PHP/Node runtimes, plus optional German source-code escrow. | GET /api/admin/compliance/sbom · SHA256SUMS.txt |
| Art. 21(2)(e) · BSIG Sec. 30(5) Security in network and information systems acquisition, development and maintenance (CVD) |
Admin-configurable RFC 9116 manifest (/.well-known/security.txt), coordinated vulnerability disclosure (< 24h triage, < 48h critical hotfix target), strict Content-Security-Policy (default-src 'self'), and 1-click SHA-256-verified in-place updates. | GET /.well-known/security.txt · SystemUpdateService |
| Art. 21(2)(f) · BSIG Sec. 30(6) Policies and procedures to assess the effectiveness of cybersecurity risk-management measures |
Scheduled daily and on-demand integrity scrubber (Nis2IntegrityHostedService) verifying stored .eml blobs against SHA-256 digests and validating the cryptographic audit hash chain across mailboxes, alongside visual DMARC/TLS-RPT analysis, external port/FCrDNS/DANE checks, and OpenTelemetry export. | POST /api/admin/compliance/scrub · /api/compliance/verify-chain |
| Art. 21(2)(g) · BSIG Sec. 30(7) Basic cyber hygiene practices and user phishing resilience |
Multi-Stage Attachment Sandbox & Deep File-Guard (magic-byte check, Office VBA/XLM/Follina decompilation, PDF /JavaScript & /Launch inspection, HTML smuggling deobfuscation, GDPR-compliant SHA-256 lookup), Content Disarm & Reconstruction (CDR), active spam, phishing and quishing defense (QR payload inspection, clicktrap detection, local-domain anti-spoofing with zero false positives on legitimate ESPs), Human Gatekeeper, and isolated Webmail sandbox preview. | ActiveSpamDefenseRuntimeService · PhishingReportService |
| Art. 21(2)(h) · BSIG Sec. 30(8) Policies and procedures regarding the use of cryptography and encryption |
TLS 1.2/1.3 across all ports with 0 ms SNI ACME, DANE/TLSA (RFC 7672), MTA-STS (RFC 8461), simultaneous Dual-DKIM (Ed25519 + RSA-2048), per-mailbox zero-knowledge encryption at rest (AES-256-GCM), built-in S/MIME and OpenPGP in Webmail (incl. WKD), and AES-256-GCM Encrypted File Share. | ServerSecretKeyring · AtRestEncryption · Dual-DKIM |
| Art. 21(2)(i) · BSIG Sec. 30(9) Human resources security, access control policies and asset management |
Multi-tenant RBAC (ServerAdmin, TenantAdmin, DomainAdmin, strictly non-mutating ComplianceAuditor), granular GAL and room visibility policies, Kerberos SSO, OIDC, SCIM 2.0 automated deprovisioning, OAuth 2.1, CIDR-restricted smk_ API keys, device inventory, and revocable per-device App Passwords. | HttpAuthHelper · ScimSupport · ApiScopeService |
| Art. 21(2)(j) · BSIG Sec. 30(10) Use of multi-factor authentication (MFA) or continuous authentication solutions |
Technically enforceable mandatory MFA policies for administrators (RequireAdminMfa with anti-lockout guard) and users (RequireUserMfa), phishing-resistant WebAuthn/FIDO2 Passkeys on both Webmail and Admin sign-in, TOTP (RFC 6238), Argon2id (64 MiB) hashing, plus email, username, or DOMAIN\user login. | PUT /api/admin/session-policy · Passkeys · TOTP |
During an active incident, meeting the statutory 24-hour early warning deadline fails when engineers must scrape disparate text logs manually. nextxch's Admin Cockpit assembles structured telemetry into a human-gated 3-stage dossier in seconds:
Captures detection timestamp, severity classification, suspected malicious/unlawful cause, and potential cross-border impact, pre-populated with correlated failed-login spikes, auto-banned IPs, and phishing reports.
Adds Indicators of Compromise (IoCs), affected accounts/protocols, live SHA-256 blob & hash-chain integrity verification results, and containment actions taken (session revocation, mandatory MFA, Campaign Vacuum Sweep).
Documents root-cause analysis, permanent technical mitigations, and full stage timestamps as an auditable Markdown or JSON dossier ready for your CISO, executive board, and national CSIRT/BSI portal.
Instead of fragile ad-hoc SQL scripts when a data-subject request arrives, core GDPR workflows ship directly in the Admin Cockpit, Account Inspector, and Webmail self-service:
NIS2 explicitly requires backup management, GoBD requires immutability and traceability, courts and auditors require documents that are demonstrably unaltered. nextxch Protect covers the technical side inside the server:
Original .eml with SHA-256 headers in a ZIP with a manifest and an Ed25519 signature, for example for court, a tax audit or an internal investigation. Recipients verify offline with nextxch-cli export verify; any change to a file is detected. Every export is recorded in the audit log. Export from Business, verification in every tier.
Incremental and encrypted with AES-256-GCM to local, SMB or S3 targets; with S3 Object Lock even a compromised administrator account cannot delete backups within the retention period. Schedules, retention and automatic verification; the catalog is readable without a running server. From Business.
Messages from the GoBD archive, from deleted items or from a backup back into the mailbox at a chosen point in time, also into a successor mailbox. The archive stays unchanged: hash, retention period and legal hold are not touched, duplicates are skipped, every run is logged. From Business.
Configuration with encrypted secrets, a version before every update, diff and partial restore with a preview. A new installation takes over configuration and data on first start; steps and denied access attempts are recorded in the audit log. Configuration in every tier, data from Business.
Where backups are stored, how often you practise the restore and who keeps the passphrase remain the operator's decision and duty. nextxch Protect on the features page
Credible compliance documentation draws an unambiguous line between software enforcement, your organization's operational governance, and third-party certification status:
Enforceable FIDO2/TOTP MFA, Argon2id, TLS 1.3/DANE/MTA-STS, Dual-DKIM, AES-256-GCM encryption at rest, daily SHA-256 blob & audit hash-chain scrubber, CycloneDX v1.5 SBOM, RFC 9116 security.txt, 24h/72h/30d CSIRT dossier builder, GDPR export/purge, GoBD WORM + procedural docs, plus encrypted data backup, configuration backup and signed evidence export.
Entity registration with national authorities where applicable, enterprise-wide ISMS policies, encrypted off-site backups with regular restore drills, physical host/datacenter security, staff awareness training, and human review + submission of incident reports to your national CSIRT.
No statutory 'NIS2 software certificate' exists under EU law. As of v1.0.0, no external penetration-test report or completed IDW PS 880 auditor certificate has been published yet (IDW PS 880 preparation is underway at iqmeta GmbH). The full compliance cockpit ships from Business (€450/yr for 250 mailboxes).
No, and any software vendor claiming automatic turnkey NIS2 certification is misleading you. NIS2 (Directive (EU) 2022/2555 and national transpositions such as German BSIG Sections 30 and 32) governs the operating entity across both technical and organizational duties (authority registration, ISMS governance, staff training, off-site backups, physical security). For your mail and groupware layer, nextxch provides the complete technical control plane out of the box: enforceable FIDO2/TOTP MFA, encryption in transit and at rest, daily SHA-256 integrity scrubbing, CycloneDX SBOM export, backup restore attestation, and 3-stage 24h/72h/30d incident dossiers.
Never. nextxch makes zero telemetry calls home and never auto-submits reports externally. The built-in BSI/CSIRT dossier engine correlates local failed logins, IP bans, phishing reports, and audit-chain state on your server into a structured 24h, 72h, or 30d draft that your CISO or DPO reviews, edits, approves, and exports as Markdown or JSON for manual submission.
Through deterministic Art. 17(3)(b) GDPR compliance: executing a GDPR hard-purge immediately deletes all unlocked messages, calendars, contacts, sessions, and orphaned storage blobs, while strictly preserving records under active statutory WORM retention or Legal Hold until their retention lock expires. The exact count of retained WORM records is documented in the purge audit response.
No. The native nextxch iOS and Android app maintains a sovereign connection directly to your own nextxch server without relaying confidential message bodies or subjects through third-party US cloud push brokers, reinforced by biometric app lock (Face ID / Touch ID / fingerprint) and an app-switcher privacy shield.
Core cryptographic security (Argon2id, TLS 1.3, DANE, MTA-STS, Dual-DKIM, 2FA/Passkeys, S/MIME, OpenPGP, and user self-service GDPR ZIP export) ships in every tier including Free. GoBD WORM archiving, per-mailbox encryption at rest, multi-tenant RBAC, GitOps Config-as-Code, the full NIS2/BSI/GDPR Admin Cockpit, and the read-only ComplianceAuditor role are included from Business (starting at €2.40 per mailbox per year) with zero add-on fees.